为您的网站量身定制的规则
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
相信网络,而不是名字 →BitFire Pro stops exploited plugins from changing your files, database, or administrator accounts - even when the vulnerability is brand new.
Runtime Application Self-Protection (RASP) checks what your application tries to do, not just the request that reached it. BitFire Pro adds authorization checks to protected file and database operations, complementing the firewall’s request filtering.
The 100% scores in this product example describe the controls assessed for that configuration, not protection against every vulnerability, and not independent certification.
探索 BitFire Pro 运行时控件 →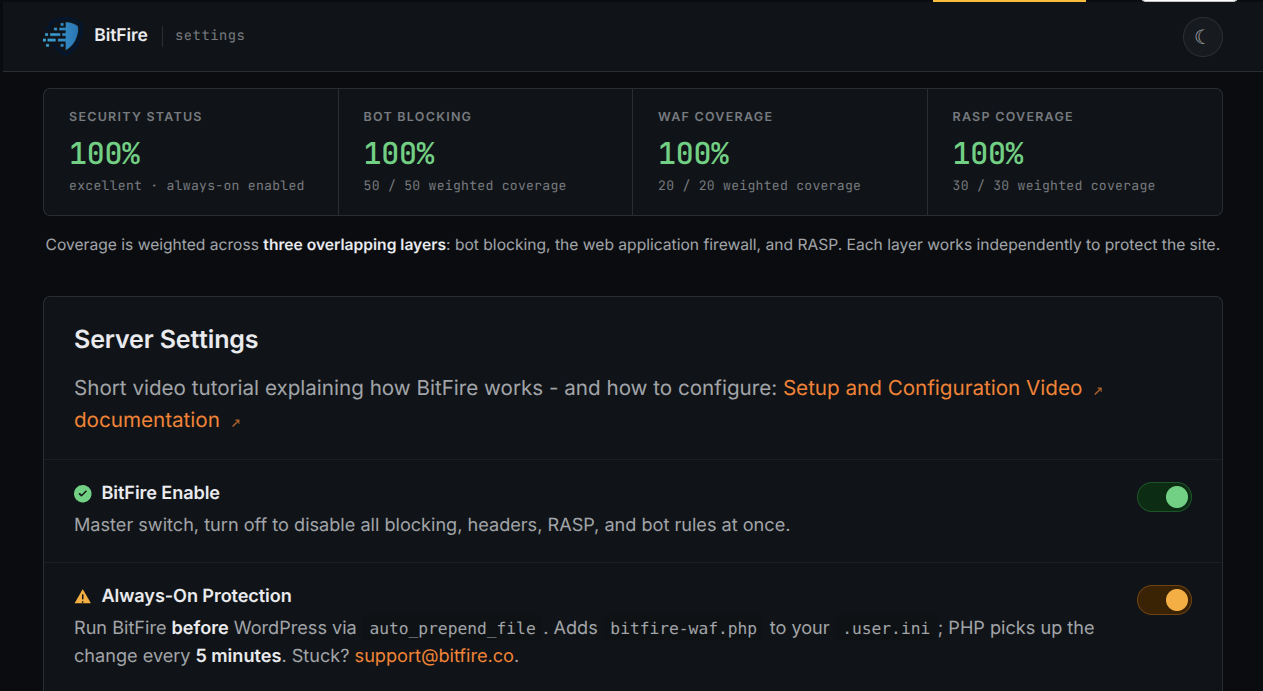
查看实际的请求过滤和 Pro 运行时保护。
三份工作,有证据来回顾所发生的事情。
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
相信网络,而不是名字 →检查受保护的 PHP 写入、数据库操作和管理员更改的授权。覆盖范围取决于启用的控件。
查看运行时控制 →行为扫描标记潜在的恶意代码。 AI 辅助分析可帮助您查看允许、修复或删除的内容。标记并不能证明感染,人工智能分析可能会出错。在更改之前查看证据并备份文件。
了解为什么它被标记 →滑动或滚动图像;展开以查看全尺寸详细信息。
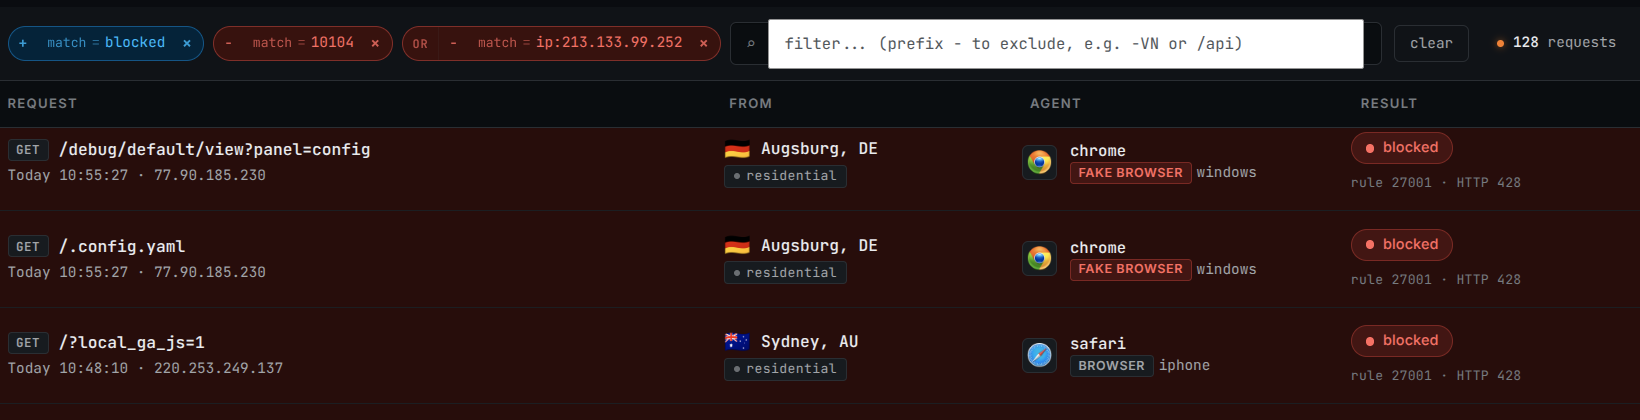
BitFire is designed to protect the places attackers target most: malicious requests, unauthorized file changes, suspicious database activity, and abusive bot traffic. Our vulnerability writeups show how those protection layers apply to real WordPress security issues.
Each example connects a known vulnerability pattern to BitFire controls that can help block exploitation, limit damage, and surface evidence for review. Use BitFire as an active protection layer while keeping WordPress, themes, and plugins updated.
| 组件 | 官方CVE记录 | CNA CVSS 3.1 | 评估 BitFire 控制 |
|---|---|---|---|
| Forminator Forms | CVE-2026-15748 正式记录CVE 发布 2026-08-18 元数据已检查 2026-09-07 |
9.8 · 严重 | 机器人策略+Pro文件保护 评估自动提交阻止和未经授权的 PHP 文件创建。结果取决于客户端策略、上传目的地和启用的控件。 |
| Meta Box AIO: MB Frontend Submission | CVE-2026-14488 正式记录CVE 发布 2026-07-29 元数据已检查 2026-09-07 |
9.1 · 严重 | Pro 数据库授权控制 评估对帖子和页面删除的授权检查。这是本文基于机制的评估,而不是重现的利用结果。 |
| WordPress Core: WP2Shell Security Vulnerability | CVE-2026-63030 正式记录CVE 发布 2026-07-17 元数据已检查 2026-09-07 |
9.8 · 严重 | 机器人策略 + WAF + Pro 管理员控制 评估客户端验证、SQL 注入检查和未经授权的管理员创建。有效性取决于策略、有效负载和受保护的操作。 |
机器人策略+Pro文件保护
评估自动提交阻止和未经授权的 PHP 文件创建。结果取决于客户端策略、上传目的地和启用的控件。
阅读分析 : Forminator FormsPro 数据库授权控制
评估对帖子和页面删除的授权检查。这是本文基于机制的评估,而不是重现的利用结果。
阅读分析 : Meta Box AIO: MB Frontend Submission机器人策略 + WAF + Pro 管理员控制
评估客户端验证、SQL 注入检查和未经授权的管理员创建。有效性取决于策略、有效负载和受保护的操作。
阅读分析 : WordPress Core: WP2Shell Security VulnerabilityBitFire helps teams secure WordPress sites, recover from threats, and keep protection in place as attacks evolve.
“有用!”
“The team at BitFire walked us through the entire install process, removed all the malware, and fully protected all our sites. I’ll never run a site without it again.”
BitFire 与 WordPress 及其 PHP 运行时集成,构建合法流量的基线,并应用您配置的保护控制。
典型的设置需要五分钟,然后是流量学习期。非商业网站免费;商业站点需要Pro。
Adaptive rules learn what your real visitors, applications, browsers, and approved bots need.
在执行前审查例外情况。 Pro 在防火墙的请求过滤中添加运行时授权检查。
BitFire Free helps add essential protection to a site. BitFire Pro adds deeper safeguards for sites where security, uptime, and active enforcement matter most.
Essential firewall, bot, and malware scan tools for sites that need a simple protection baseline.
Deeper protection for sites that want stronger assurance, runtime enforcement, scheduled scanning, and more security visibility.
让 BitFire 负责安装和持续维护。
Want help choosing the right protection level or support option? Talk with a security engineer about your site, risks, and operating needs.
对于网站所有者、机构和安全团队: 探索产品组合和企业用例 →
This compares control boundaries, not named products, their current features, or test results.
| 控制边界 | 请求过滤 | Runtime enforcement |
|---|---|---|
| 主要问题 | 该请求是否应该到达应用程序? | 这个受保护的操作是否被授权? |
| 信号 | 请求内容、客户端身份和流量策略 | 应用程序身份、权限和尝试的操作 |
| 执行点 | 在请求到达易受攻击的处理程序之前 | 当应用程序代码尝试受保护的操作时 |
| BitFire 中的示例 | 机器人策略和 SQL-注入请求检查 | Pro 检查受保护的 PHP 写入和管理员更改 |
| 限制 | 覆盖范围取决于检查、规则和例外情况 | 覆盖范围取决于支持的操作、配置和授权上下文 |
这两层都不能取代修补、访问控制或恢复计划。 查看 BitFire 记录的控制和配置要求 →
Need to evaluate BitFire for a specific stack? Talk directly with a security engineer.
Talk to a security engineer开销取决于托管、PHP 和插件活动、启用的控件、流量和缓存状态。我们不会在这里发布固定的延迟数字,因为此页面没有可重复的基准报告。
Recommended measurement procedure, not a published test result:
Start protecting a site in minutes, or bring us your architecture and security requirements for a technical walkthrough.
Protect my site freePro正在保护商业网站吗? 查看Pro.