Rules tailored to your site
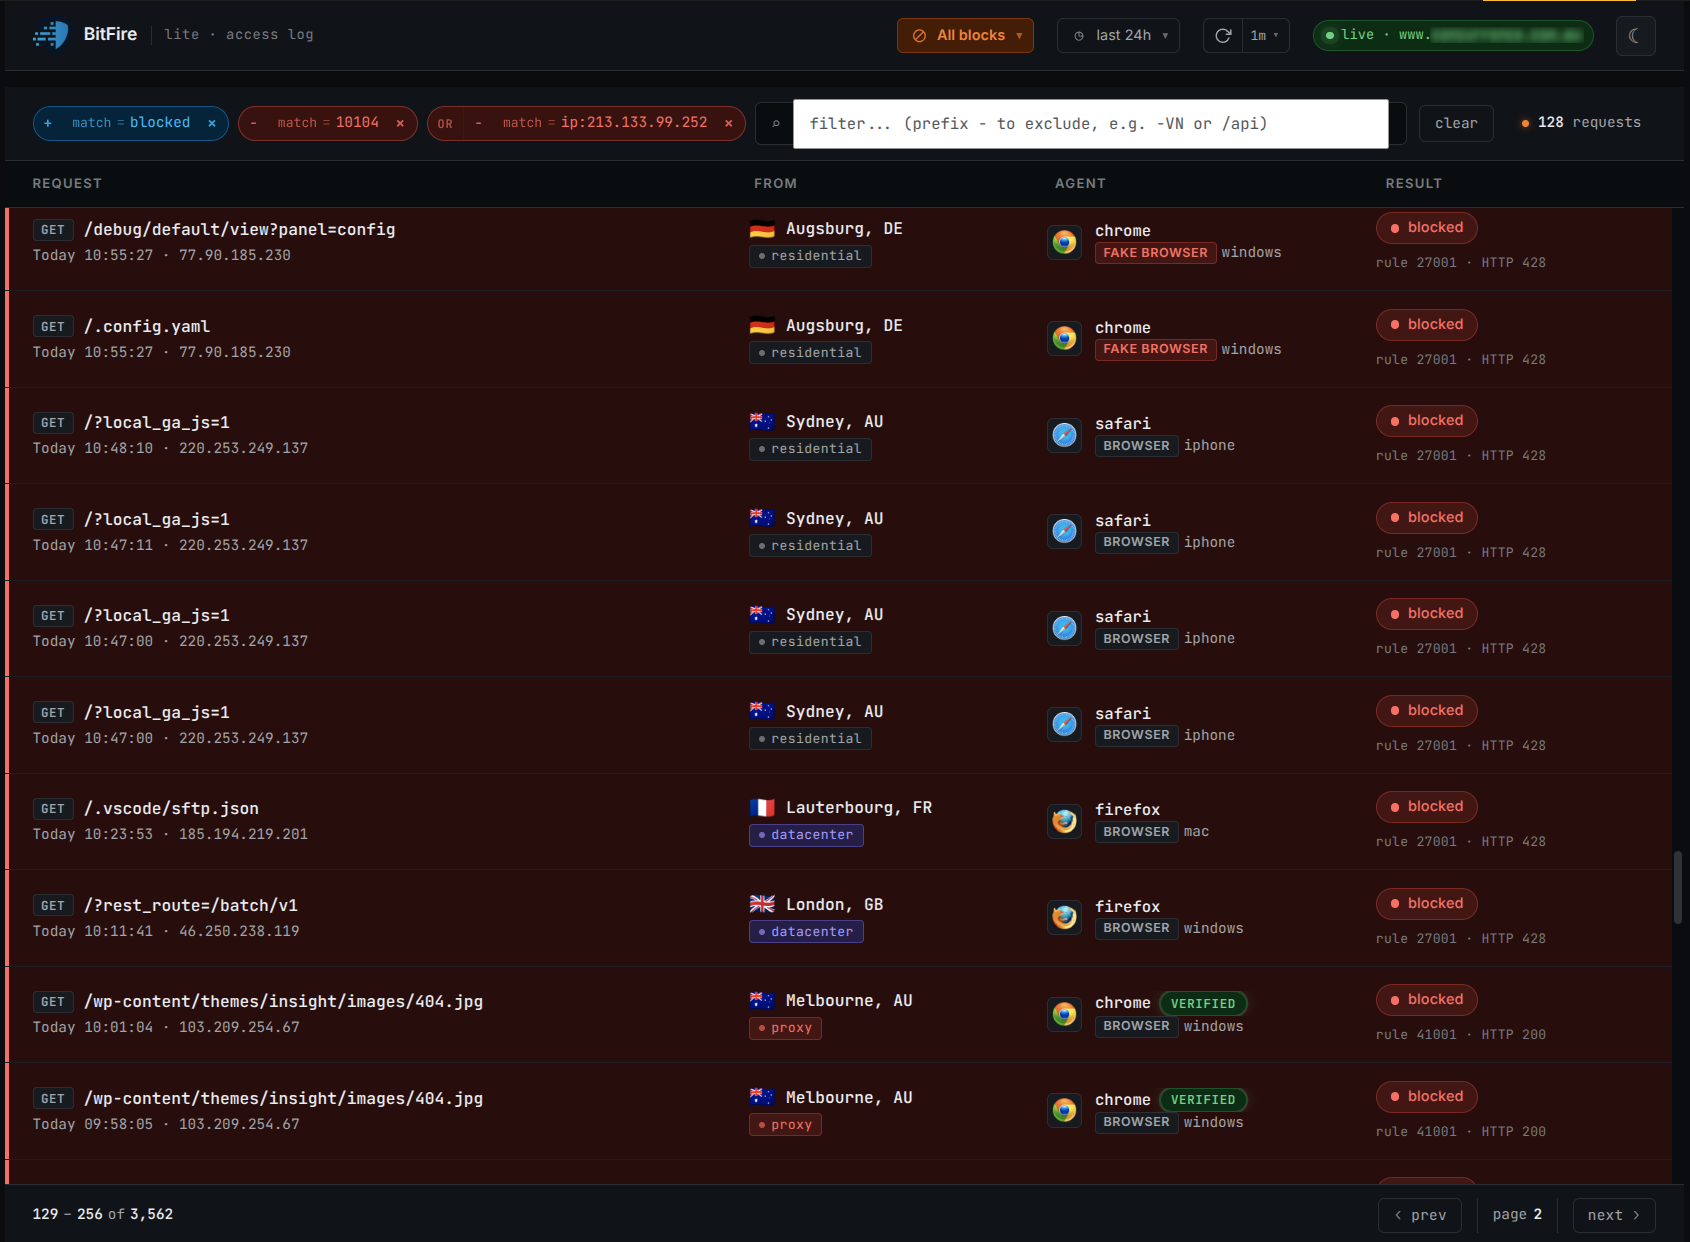
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
Trust the network, not the name →BitFire Pro stops exploited plugins from changing your files, database, or administrator accounts - even when the vulnerability is brand new.
Runtime Application Self-Protection (RASP) checks what your application tries to do, not just the request that reached it. BitFire Pro adds authorization checks to protected file and database operations, complementing the firewall’s request filtering.
The 100% scores in this product example describe the controls assessed for that configuration, not protection against every vulnerability, and not independent certification.
Explore BitFire Pro runtime controls →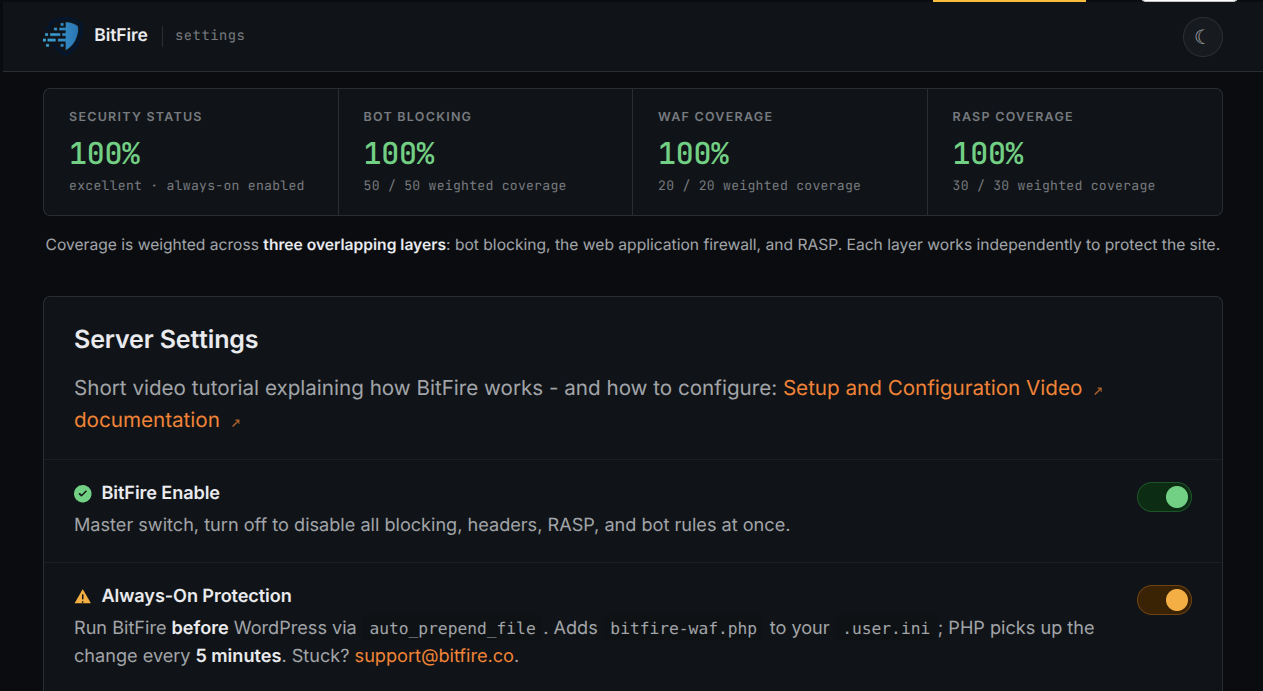
See request filtering and Pro runtime protection in action.
Three jobs, with the evidence to review what happened.
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
Trust the network, not the name →Check authorization for protected PHP writes, database operations, and administrator changes. Coverage depends on enabled controls.
Review runtime controls →Behavioral scanning flags potentially malicious code. AI-assisted analysis helps you review what to allow, repair, or remove. A flag is not proof of infection, and AI analysis can be mistaken. Review evidence and back up files before changes.
Understand why it was flagged →Swipe or scroll across the image; expand for full-size details.
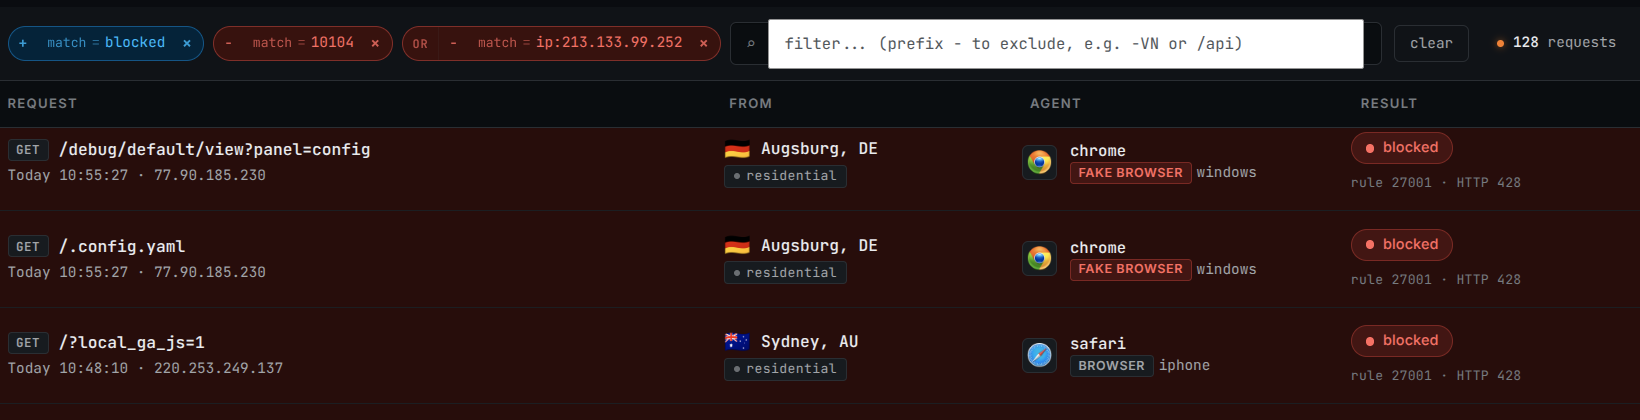
BitFire is designed to protect the places attackers target most: malicious requests, unauthorized file changes, suspicious database activity, and abusive bot traffic. Our vulnerability writeups show how those protection layers apply to real WordPress security issues.
Each example connects a known vulnerability pattern to BitFire controls that can help block exploitation, limit damage, and surface evidence for review. Use BitFire as an active protection layer while keeping WordPress, themes, and plugins updated.
| Component | Official CVE record | CNA CVSS 3.1 | Assessed BitFire controls |
|---|---|---|---|
| Forminator Forms | CVE-2026-92229 official recordCVE published 2026-09-19 Metadata checked 2026-09-21 |
9.1 · Critical | Bot policy + Pro runtime controls Assesses automated Forminator exploit delivery and unauthorized privileged actions invoked through injected shortcodes. Results depend on client policy, shortcode behavior, and enabled runtime controls. |
| The Events Calendar | CVE-2026-78159 official recordCVE published 2026-09-12 Metadata checked 2026-09-21 |
9.8 · Critical | Bot policy + Pro file and administrator controls Assesses automated comment-delivery blocking and unauthorized PHP-file or administrator persistence after callable injection. Results depend on comment reachability, client policy, and enabled runtime controls. |
| JetFormBuilder | CVE-2026-12793 official recordCVE published 2026-09-16 Metadata checked 2026-09-21 |
9.8 · Critical | Bot policy + Pro administrator controls Assesses automated JetFormBuilder exploit delivery and unauthorized administrator account creation. Results depend on schema reachability, client policy, and enabled runtime controls. |
Bot policy + Pro runtime controls
Assesses automated Forminator exploit delivery and unauthorized privileged actions invoked through injected shortcodes. Results depend on client policy, shortcode behavior, and enabled runtime controls.
Read analysis : Forminator FormsBot policy + Pro file and administrator controls
Assesses automated comment-delivery blocking and unauthorized PHP-file or administrator persistence after callable injection. Results depend on comment reachability, client policy, and enabled runtime controls.
Read analysis : The Events CalendarBot policy + Pro administrator controls
Assesses automated JetFormBuilder exploit delivery and unauthorized administrator account creation. Results depend on schema reachability, client policy, and enabled runtime controls.
Read analysis : JetFormBuilderBitFire helps teams secure WordPress sites, recover from threats, and keep protection in place as attacks evolve.
“It works!”
“The team at BitFire walked us through the entire install process, removed all the malware, and fully protected all our sites. I’ll never run a site without it again.”
BitFire integrates with WordPress and its PHP runtime, builds a baseline of legitimate traffic, and applies your configured protection controls.
Typical setup takes five minutes, followed by a traffic-learning period. Free for non-commercial sites; business sites require Pro.
Adaptive rules learn what your real visitors, applications, browsers, and approved bots need.
Review exceptions before enforcement. Pro adds runtime authorization checks to the firewall’s request filtering.
BitFire Free helps add essential protection to a site. BitFire Pro adds deeper safeguards for sites where security, uptime, and active enforcement matter most.
Essential firewall, bot, and malware scan tools for sites that need a simple protection baseline.
Deeper protection for sites that want stronger assurance, runtime enforcement, scheduled scanning, and more security visibility.
Let BitFire handle installation and ongoing care.
Want help choosing the right protection level or support option? Talk with a security engineer about your site, risks, and operating needs.
Explore the details: protection features · malware scanning · licensing and support.
For site owners, agencies, and security teams: explore portfolio and enterprise use cases →
This compares control boundaries, not named products, their current features, or test results.
| Control boundary | Request filtering | Runtime enforcement |
|---|---|---|
| Main question | Should this request reach the application? | Is this protected operation authorized? |
| Signals | Request content, client identity, and traffic policy | Application identity, permissions, and the operation attempted |
| Enforcement point | Before the request reaches the vulnerable handler | When application code attempts a protected action |
| Examples in BitFire | Bot policies and SQL-injection request inspection | Pro checks on protected PHP writes and administrator changes |
| Limits | Coverage depends on inspection, rules, and exceptions | Coverage depends on supported operations, configuration, and authorization context |
Neither layer replaces patching, access control, or recovery planning. Review BitFire’s documented controls and configuration requirements →
Need to evaluate BitFire for a specific stack? Talk directly with a security engineer.
Talk to a security engineerOverhead depends on hosting, PHP and plugin activity, enabled controls, traffic, and cache state. We do not publish a fixed latency figure here because a reproducible benchmark report is not available for this page.
Recommended measurement procedure, not a published test result:
Start protecting a site in minutes, or bring us your architecture and security requirements for a technical walkthrough.
Protect my site freeProtecting a business site? View Pro.