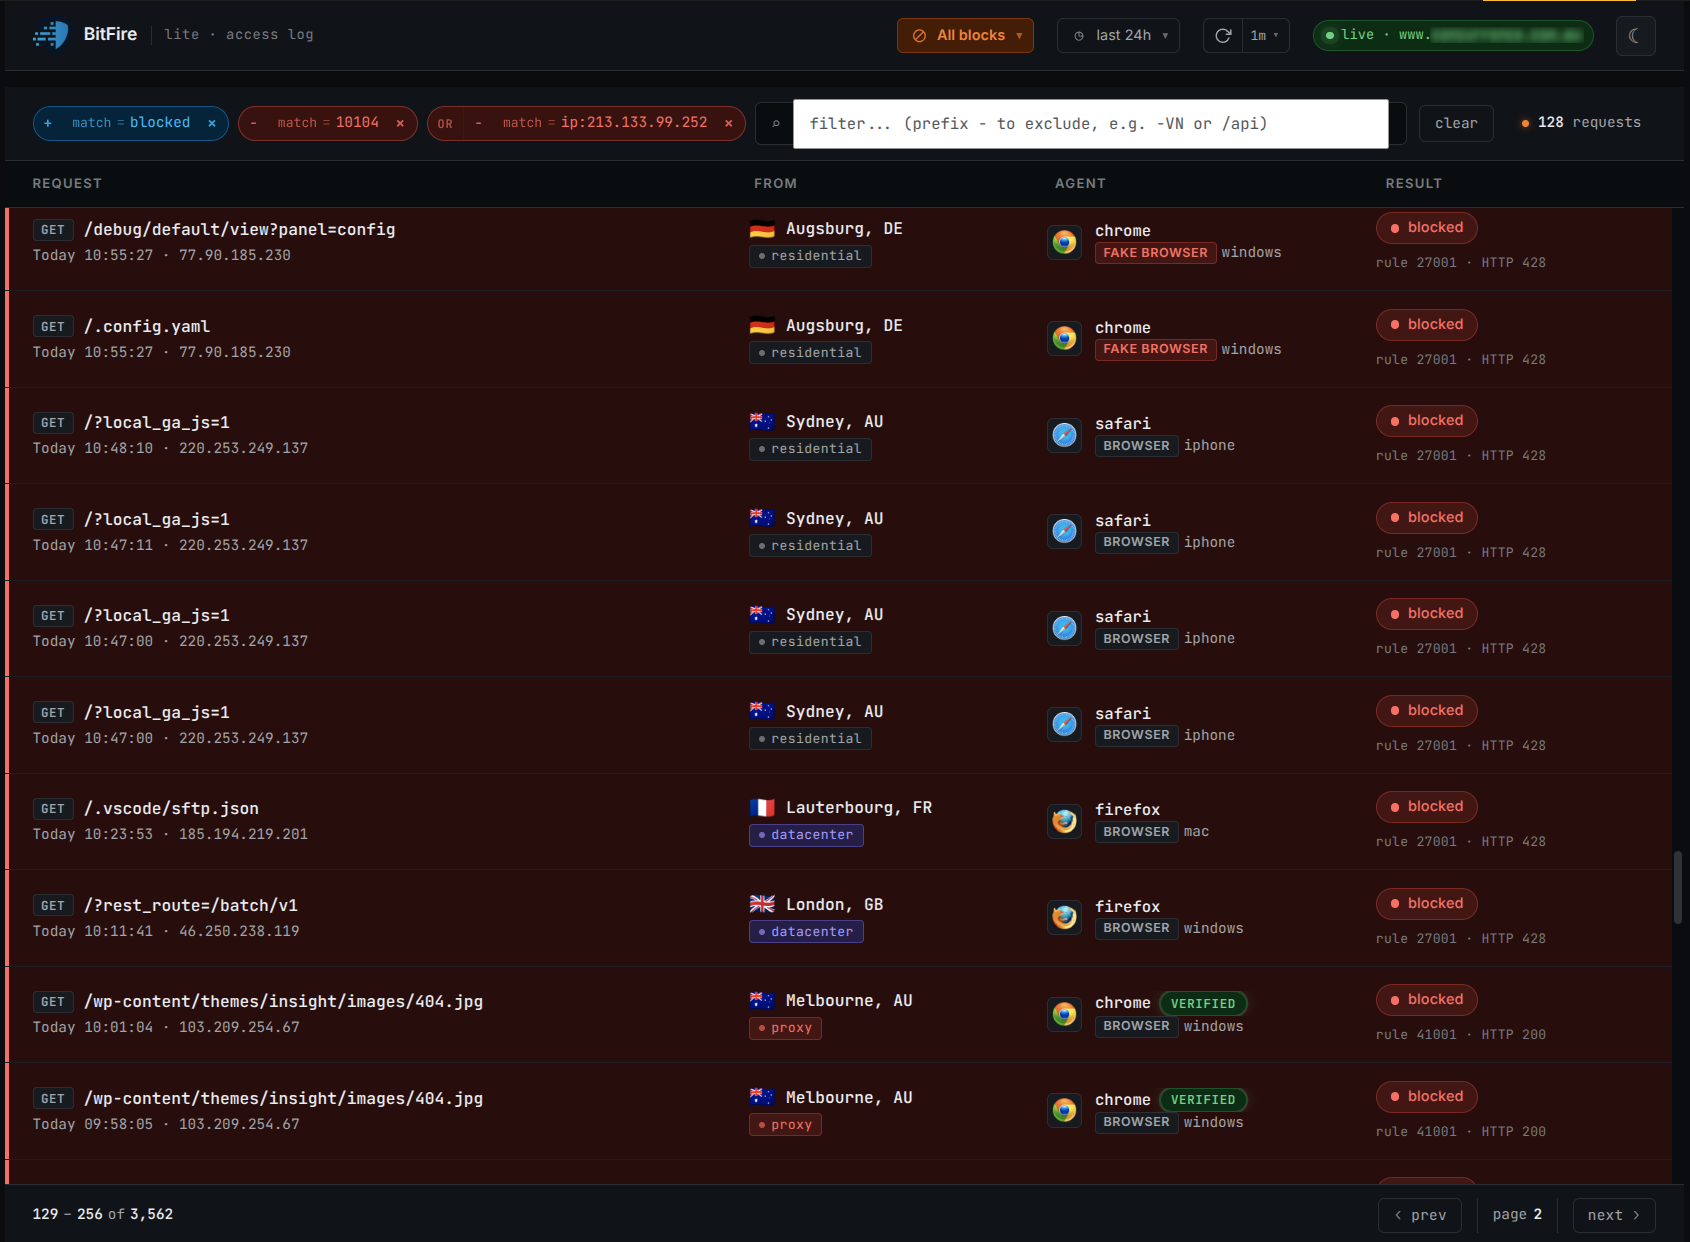
为您的网站量身定制的规则
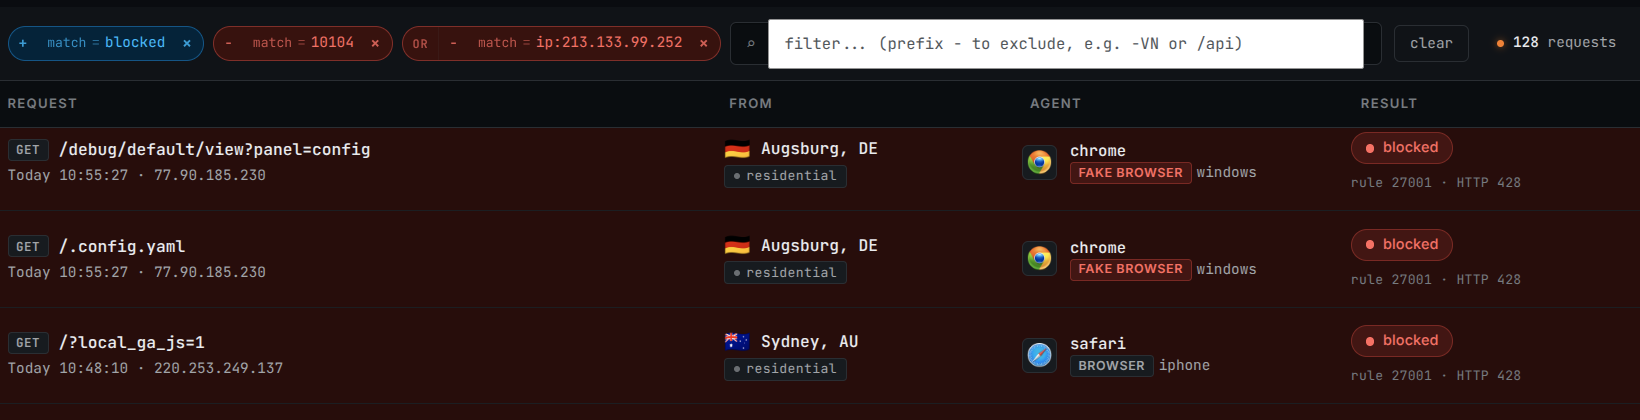
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
相信网络,而不是名字 →BitFire Pro stops exploited plugins from changing your files, database, or administrator accounts - even when the vulnerability is brand new.
Typical setup: 5 minutes · No credit card required · View Pro runtime controls
BitFire Pro checks protected file, database, and administrator operations inside WordPress, helping stop plugin and theme vulnerabilities before they become site damage.
探索 BitFire Pro 运行时控件 →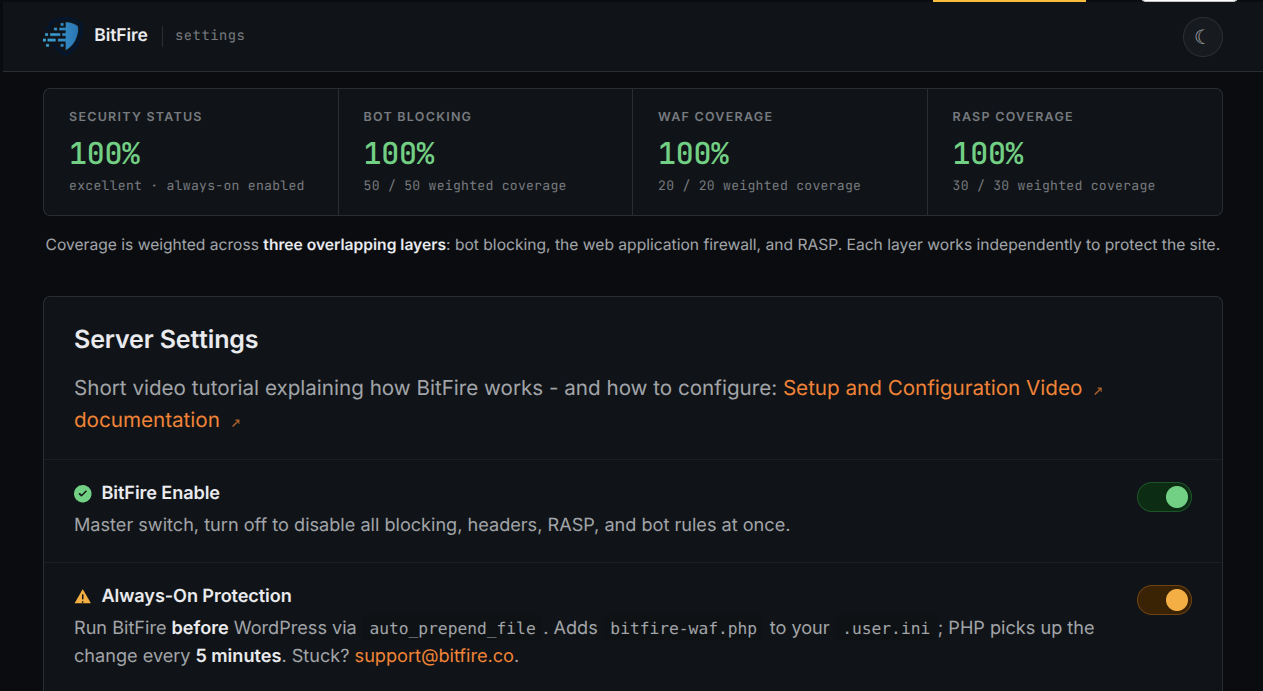
Start with the edge. Add runtime controls where compromise actually happens.
Inspect malicious input, review traffic exceptions, and apply bot policies using available network evidence, not a user-agent alone.
相信网络,而不是名字 →Check authorization for protected PHP writes, database operations, and administrator changes. Coverage depends on enabled controls.
查看运行时控制 →Behavioral scanning flags potentially malicious code. AI-assisted analysis helps you review what to allow, repair, or remove. A flag is not proof of infection, and AI analysis can be mistaken. Review evidence and back up files before changes.
了解为什么它被标记 →滑动或滚动图像;展开以查看全尺寸详细信息。
BitFire helps stop real WordPress attack paths before they become file changes, database damage, or administrator takeover.
| 组件 | CVE and install base | CNA CVSS 3.1 | 评估 BitFire 控制 |
|---|---|---|---|
| HT Contact Form | CVE-2026-96326 technical analysisInstall base: 10000 | — · 未审核 |
参见文章的控制评估
本文尚未经过主页证据摘要审核。 |
| ConvertPlus | CVE-2026-87741 technical analysisInstall base: Not publicly reported | — · 未审核 |
参见文章的控制评估
本文尚未经过主页证据摘要审核。 |
| Automatic.css | CVE-2026-15273 technical analysisInstall base: Not publicly reported | — · 未审核 |
参见文章的控制评估
本文尚未经过主页证据摘要审核。 |
参见文章的控制评估
本文尚未经过主页证据摘要审核。
阅读分析 : HT Contact Form参见文章的控制评估
本文尚未经过主页证据摘要审核。
阅读分析 : ConvertPlus参见文章的控制评估
本文尚未经过主页证据摘要审核。
阅读分析 : Automatic.css
“there is only one thing to say: It works! And this is the only firewall [to] realy do the job. In the pro version you [will] get all you need.”摘自客户的评论。
“The team at BitFire walked us through the entire install process, removed all the malware, and fully protected all our sites. I’ll never run a site without it again.”
Free covers the baseline. Pro is recommended for commercial sites that need protected file, database, and administrator operations checked inside WordPress.
Essential firewall, bot, and malware scan tools for sites that need a simple protection baseline.
Recommended for commercial and business-critical sites that need runtime enforcement, scheduled scanning, and deeper security visibility.
BitFire filters requests, Pro adds runtime checks, and no layer replaces patching, access control, backups, or recovery planning.
Overhead depends on hosting, PHP and plugin activity, enabled controls, traffic, and cache state.
Recommended measurement procedure, not a published test result: use an isolated staging copy, record versions and enabled controls, run the same representative requests, and compare baseline, firewall/bot controls, and Pro runtime controls separately.
Install the free baseline now, or send your site context for a focused technical walkthrough.
Protect my site freeRunning a commercial site? You can start free, but we recommend Pro for runtime controls.