CVE-2026-15273 vulnerability and BitFire protection

How BitFire Blocks CVE-2026-15273: Automatic.css Stored XSS

WordPress vulnerability research

BitFire's WAF inspects request URLs and blocks the Cross-Site Scripting payloads CVE-2026-15273 lets attackers store in Automatic.css 4.0.0.

Unauthenticated attacker Medium severity (CVSS 6.4) Script execution in an admin browser Stored Cross-Site Scripting
BitFire · Vulnerability advisoryResearch published
AdvisoryCVE-2026-15273
ComponentAutomatic.css
Executive summary

What WordPress administrators need to know

CVE-2026-15273 gives unauthenticated attackers a stored script injection into WordPress sites running Automatic.css 4.0.0: the plugin stores an attacker-controlled REQUEST_URI without sufficient sanitization, and the payload executes in an administrator's browser whenever the Activity Log settings page is opened. BitFire stops this attack at the front door. The BitFire WAF inspects request URLs and query strings before WordPress processes them and blocks Cross-Site Scripting payloads delivered in that data, so the script is never stored and never executed. Patch to 4.0.1, and run BitFire Threat Hunter if version 4.0.0 was ever live on your site.

At a glance

Key facts

  • Stored Cross-Site Scripting in Automatic.css via the REQUEST_URI value
  • Insufficient input sanitization and output escaping affects every 4.0.0 release
  • Unauthenticated attackers can inject arbitrary web scripts with a single crafted request
  • Payloads execute when an administrator opens the Activity Log settings page
  • Version 4.0.1 is the vendor-identified fixed release
  • The BitFire WAF inspects request URLs and blocks script payloads before they are stored
01
Vulnerability overview

Understand the exposure

The affected component, attack path, and practical risk for WordPress websites.

Affected componentAutomatic.css
Potential reachNot publicly reported installations
Attack techniquestored cross-site scripting
Published2026-09-29
The exploit travels in the request URL itself — exactly where the BitFire WAF inspects. A Cross-Site Scripting payload in REQUEST_URI is detected and blocked before Automatic.css can store it.
02
Technical analysis

How the vulnerability works

Research details, affected versions, exploitation behavior, and remediation guidance.

What CVE-2026-15273 Establishes

Automatic.css for WordPress is vulnerable to Stored Cross-Site Scripting in every 4.0.0 release. The plugin accepts the REQUEST_URI value with insufficient input sanitization and outputs it without proper escaping, so an unauthenticated attacker can plant arbitrary web scripts that the plugin stores. No credentials, session, or victim cooperation is required on the attacker's side beyond one crafted request. The stored script then executes whenever an administrator accesses the plugin's Activity Log settings page — attacker-chosen code running inside a privileged browser session. Version 4.0.1 is the release the vendor identifies as fixed.

BitFire FREE WAF: The Payload Is Blocked Before It Is Stored

This exploit lives or dies at the request layer, and that is exactly where BitFire inspects it. Before WordPress or Automatic.css processes anything, the BitFire WAF examines request URLs and query strings — and REQUEST_URI is the request URL itself. Its Cross-Site Scripting detection identifies malicious script payloads in inspected request data and blocks the request outright. The injection step of this chain is a documented exploit requirement, and BitFire removes it: nothing is stored, so nothing renders inside an administrator's browser. BitFire FREE delivers this WAF protection for eligible non-commercial sites; commercial sites require the appropriate commercial license.

If Your Site Was Affected, Investigate for Persistence

Patching to 4.0.1 closes the injection point, but it does nothing about a script that already executed in an administrator's browser. If Automatic.css 4.0.0 was installed while any administrator visited the Activity Log settings page, treat the site as potentially compromised and investigate immediately. BitFire Threat Hunter performs a thorough post-compromise investigation: it hunts backdoor administrator accounts, hidden database triggers, WordPress and server cron persistence, must-use plugins and startup-chain modifications, long-running PHP processes, and the droppers that can restore malware after cleanup. Remove every persistence mechanism it finds and rotate administrator credentials. A site that looks clean on the surface is not proven clean — investigate before you trust it.

Patch Today, Defend in Depth

Update Automatic.css to 4.0.1 today and make BitFire part of the same response. BitFire's WAF stands between unauthenticated attackers and this injection point, and BitFire Threat Hunter is ready if the plugin ran exposed before protection was in place. There is no reason to keep running an unauthenticated, admin-targeted script injection when a fixed release is available. Install or enable BitFire, patch to 4.0.1, and run a Threat Hunter investigation on any site that hosted version 4.0.0 — then let this CVE end as a non-event.

03
Zero-day protection

Protection from the first exploit request

BitFire protects WordPress servers on day zero—before a vulnerability is publicly known and before other vendors have time to develop signatures or patches.

01 · VerifyStop unknown clients

Bot controls and browser verification stop untrusted automated clients before previously unknown exploit code reaches WordPress.

02 · DetectBlock malicious behavior

General WAF protections identify dangerous request behavior and hostile payloads without waiting for a vulnerability-specific signature.

03 · PreventContain attacks at runtime

RASP follows execution inside PHP and prevents unauthorized changes to protected files, accounts, and database content.

BitFire · WordPress protectionZero-day ready
BitFire zero-day WordPress vulnerability protection
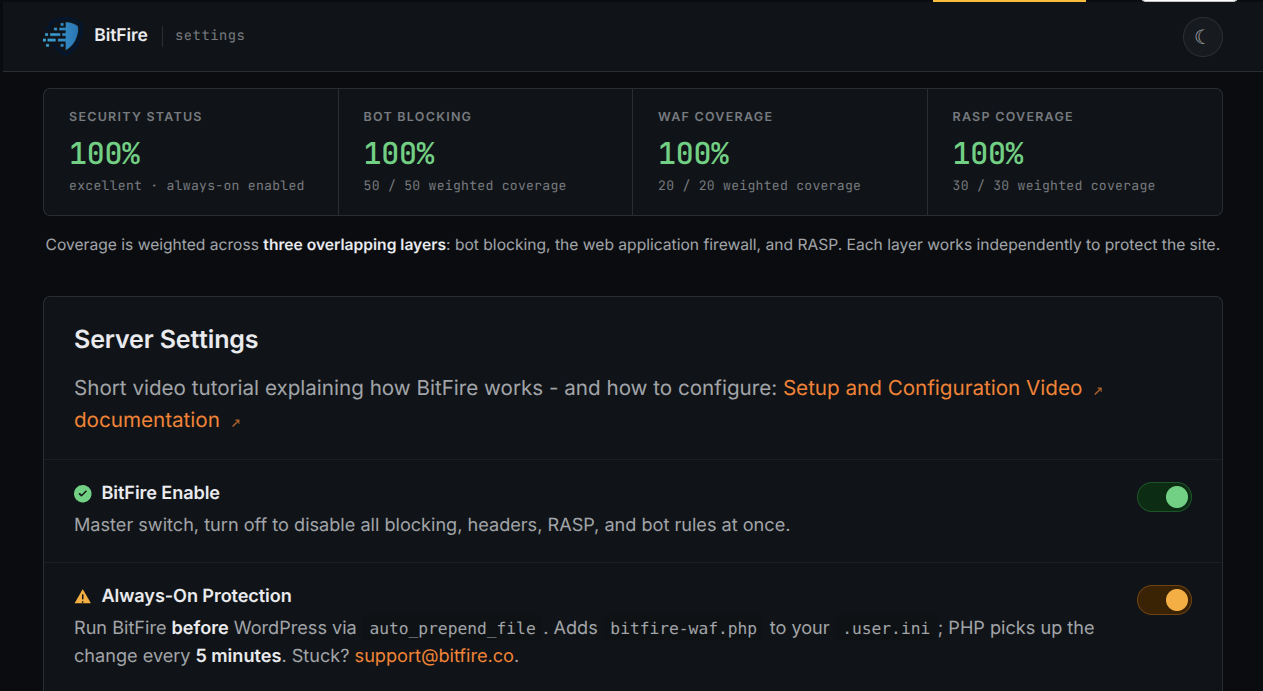
BitFire combines verified-client controls, behavior-based WAF detection, and runtime RASP enforcement to protect WordPress before an exploit has a name, CVE, signature, or vendor patch.
About the author

Cory Marsh

Cory has more than 20 years of internet security experience and is a lead developer on the BitFire project.

Read BitFire security research →
Protect your WordPress website

Add protection before the next exploit arrives.

BitFire combines bot controls, request inspection, malware detection, and runtime protection in one WordPress security platform.

Protect my site free →