
RASP保护
When enabled, BitFire runtime application self-protection (RASP) controls evaluate supported operations against the request’s authorization context—even when the exploit is new.
查看三个控件When enabled, PRO runtime controls can block supported file, database, and administrator operations when a request lacks the required authority. Protection applies within each control’s documented coverage. Then investigate persistence beyond ordinary file scans with Threat Hunter and AI-assisted malware analysis.
Coverage depends on the enabled control, supported operation, and request authorization context. Review runtime-control coverage.
BitFire FREE can protect commercial sites. Choose PRO when enabled runtime controls, deeper persistence investigation, or BitFire-managed operation matter to the site.
Read FREE and PRO licensing guidancePRO 将攻击期间的执法与可疑活动后的更深入调查结合起来。它是为那些妥协会带来实际业务成本的网站而设计的。
When enabled, BitFire runtime application self-protection (RASP) controls evaluate supported operations against the request’s authorization context—even when the exploit is new.
查看三个控件检查数据库内容、WordPress cron 作业、数据库触发器、必须使用的插件、启动链和后台 PHP 进程以进行持久性正常文件扫描看不到。
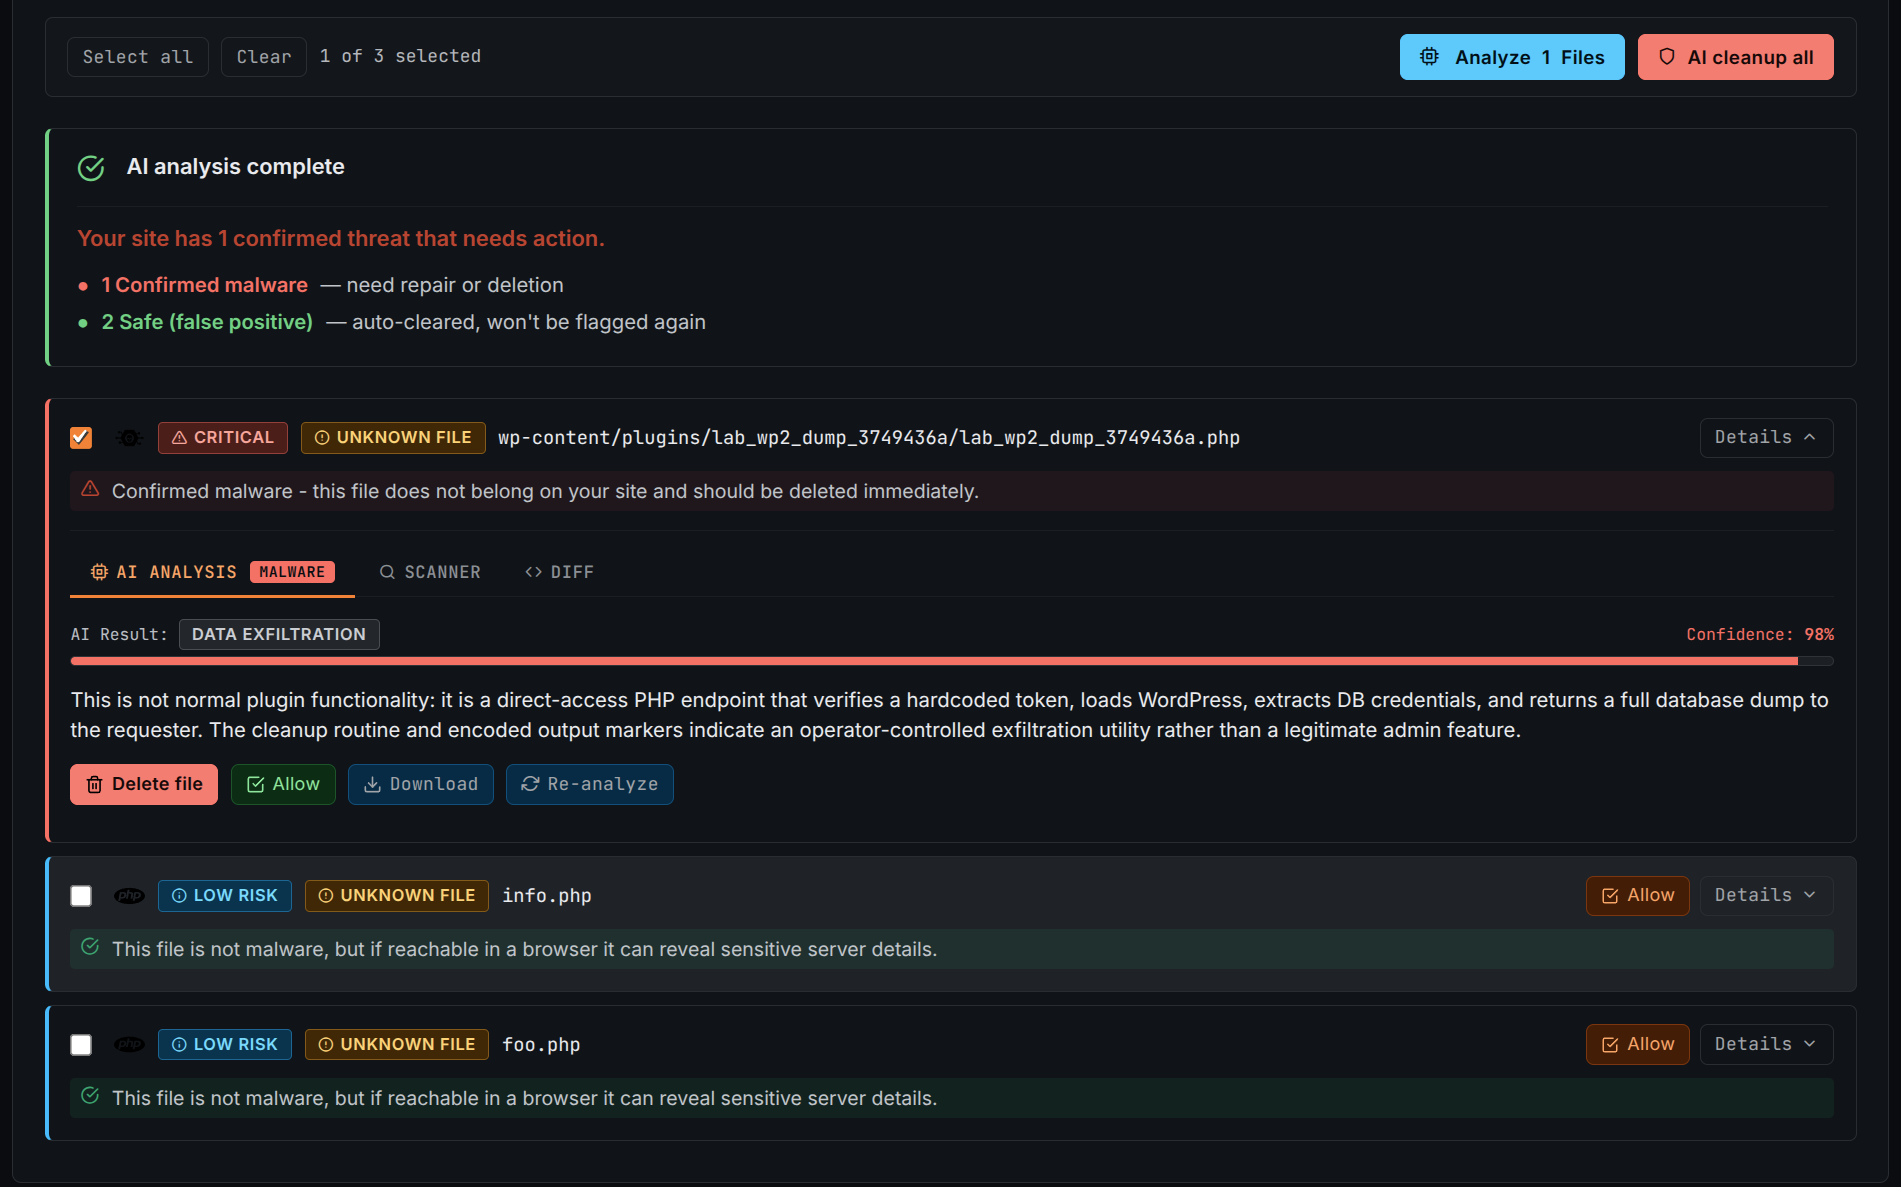
探索威胁猎手Use 1,000 AI credits for an assisted review of suspicious code, understand why it was flagged, and make a more informed allow, repair, or delete decision. AI output is evidence to review, not proof by itself.
阅读扫描仪指南WAF 询问请求是否看起来是恶意的。 BitFire RASP 还会询问该请求是否有权在 WordPress 内执行危险操作。
When the filesystem control is enabled, BitFire uses a PHP stream wrapper to evaluate supported writes to .php files. A write is blocked when the active request lacks the required administrator authorization.
When the database control is enabled, BitFire evaluates supported user-creation and privilege-change queries. The update is blocked when the request lacks the required administrator authorization.
阻止流氓管理员帐户When this control is enabled, BitFire evaluates supported attempts to impersonate an administrator. Impersonation is blocked when the requesting session lacks the required administrator authorization.
阻止身份验证绕过威胁猎手超越了普通的文件系统扫描,以查找攻击者用于在清理后幸存并在以后重新获得控制权的机制。
为什么它很重要: 在每个恶意 PHP 文件似乎被删除后,后台进程、计划任务、触发器或存储的脚本可能会重新感染站点。
Add the WordPress domains you want to protect, then choose self-management, BitFire-managed operation, or around-the-clock priority support.
有我们未提及的许可或兼容性问题吗?直接与 BitFire 团队交谈。
联系 BitFirePRO unlocks 1,000 AI malware analysis credits, advanced Threat Hunter audits, and enabled RASP controls for supported filesystem, database, and administrator impersonation operations.
BitFire FREE can protect commercial websites. Choose PRO when the site needs enabled runtime controls for supported file, database, and administrator operations, deeper persistence investigation with Threat Hunter, scheduled analysis, or BitFire-managed operation.
One license covers one domain. Portfolio discounts begin at 2 sites, and the matching tier applies to every license in the proposed order. The domain list controls the quantity so there are no unassigned licenses. For example, 10 sites at $28.00 per site is $280.00 per year before an optional per-site management package.
BitFire 使用默认阻止的安全模型。这减少了允许未知或未经授权的活动的机会,但某些合法流量最初可能会被阻止。这些请求必须经过审查和批准,以便网站能够履行其预期功能,而不会不必要地削弱保护。
Managed Protection is the hands-off option: BitFire handles installation, configuration, maintenance, monitoring, and operational tuning during normal U.S. business hours for $200 per site per year. Choose Self-managed if your team prefers direct control with guided setup. 优先支持 adds 24/7 coverage and a one-hour response time for any issue for $450 per site per year.
The published schedule beside the calculator shows upcoming single-site rates. The displayed rate is reserved for the 24-hour email-verification window, and portfolio discounts apply to every license in the order. Each activated license remains valid for one year; renewal pricing is handled separately.
No. When an applicable RASP control is enabled, BitFire evaluates the authorization behind supported protected operations. An unknown exploit can still be blocked when it attempts a supported PHP write, administrator privilege change, or administrator impersonation without the required authorization.
Threat Hunter 检查普通恶意软件文件之外的持久性,包括数据库内容、cron 任务、MySQL 触发器、WordPress 启动链、必须使用的插件、管理员帐户和后台 PHP 进程。
Add enabled runtime controls, deeper persistence investigation, and AI-assisted malware analysis to every site you manage.