Unauthenticated Authorization Bypass to Arbitrary Plugin Installation
CleanTalk's remote-call handler registers on WordPress's public init hook, so every visitor reaches it unauthenticated, and every parameter — action, plugin name, token, API key, target plugin — arrives from $_REQUEST. RemoteCalls::perform() authorizes a call with a valid token or through checkWithoutToken() plus a tokenless action allow-list. In 6.71, checkWithoutToken() treated the raw reverse-DNS (PTR) hostname of the connecting IP as proof of CleanTalk NOC identity, with no forward confirmation. PTR records belong to whoever controls the address — routinely a rented server's operator. On sites whose CleanTalk API key is invalid or missing, one unverified hostname satisfies the NOC branch: an attacker-controlled value crossing straight into an authorization decision.
BitFire FREE Bot Protection Stops the Exploit Before WordPress Runs It
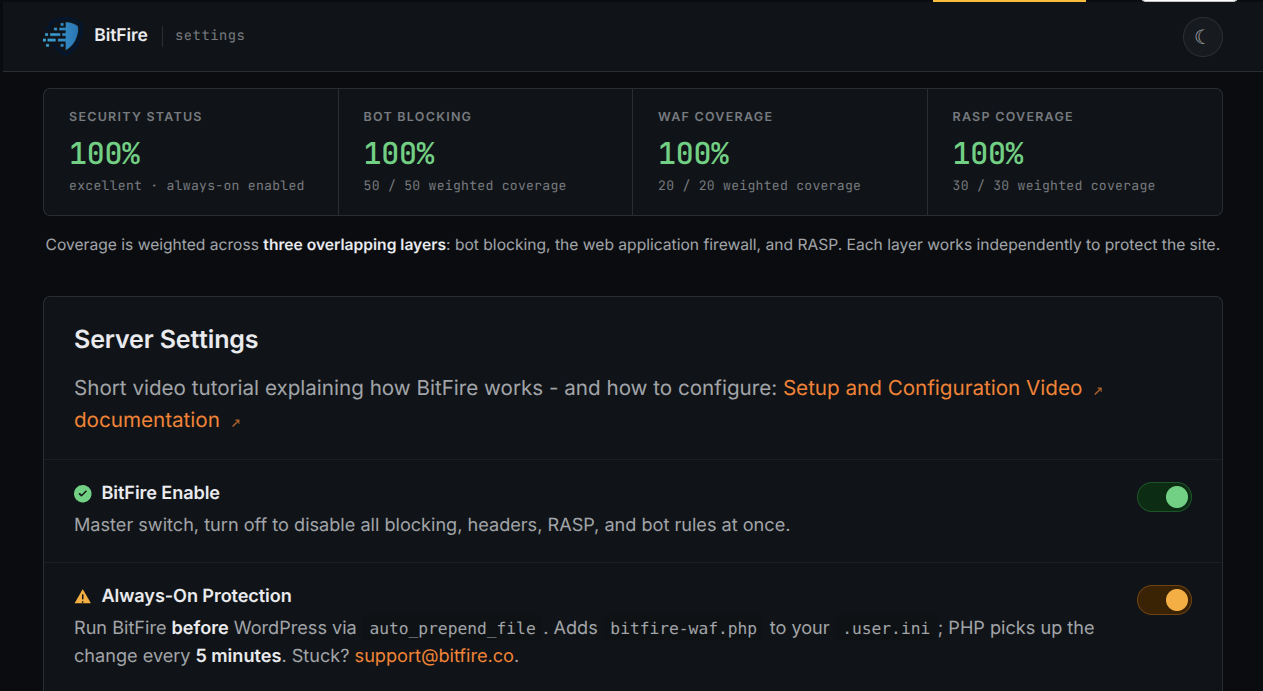
Every step of this chain travels in scripted, unauthenticated HTTP requests — precisely the traffic BitFire FREE Bot Protection refuses. Unknown or restricted automated clients are barred from POSTing data and calling sensitive plugin endpoints, so the spoofed NOC remote call never reaches checkWithoutToken(). Known attack and scanning tools are blocked outright, and clients presenting as browsers must pass JavaScript browser verification that scripts and fake browsers routinely fail. The chain dies at delivery: no request, no authorization decision, no planted key. The documented caveat: explicitly allowlisted bots and successfully verified real browsers are not categorically stopped — which is exactly why a second layer matters.
BitFire PRO RASP Blocks the Unauthorized Plugin Install
If a crafted request ever slipped past request filtering, BitFire PRO RASP evaluates what WordPress attempts, not what the request looks like. Its filesystem protection inspects PHP-file writes and blocks unauthorized creation or modification of PHP, explicitly including plugin installation payloads. The moment apbct_rc__install_plugin() drives CleantalkUpgrader to unpack attacker-selected code under wp-content/plugins, RASP stops the write: no attacker PHP reaches disk, so activate_plugins() has nothing hostile to arm. This enforcement sits at the protected operation, requires no CVE signature, and applies to any unauthenticated or non-administrator request pursuing the same outcome. Runtime blocking is BitFire PRO — enable RASP filesystem protection in production.
Update to 6.72: Forward-Confirmed DNS Breaks the Chain at Entry
Version 6.72 rewrites Helper::ipResolve() to perform Forward-Confirmed reverse DNS: validate the IP, take the PTR hostname, resolve it forward, and require the original IP among the answers — every failure returns false. checkWithoutToken() now rejects an unresolvable client and demands a strictly verified NOC hostname. With PTR spoofing dead, the tokenless NOC branch is unreachable, no attacker-known API key can be planted, and no valid remote-call token can be derived for the privileged plugin actions. Sites running 6.71 or earlier should update immediately; there is no configuration workaround for a flaw this early in the authorization chain.
If Your Site Was Affected, Investigate for Persistence
Patching closes CVE-2026-1490; it does not undo an earlier compromise. An attacker who completed the chain had working plugin installation on your server — assume persistence and hunt for it. BitFire Threat Hunter performs a thorough post-compromise investigation: it discovers backdoor WordPress administrator accounts, hidden database triggers, long-running PHP processes, and droppers that can restore malware or reinfect the site. Run it on every site that ran 6.71 or earlier, remove every item it finds, and rotate WordPress salts and administrator credentials. A quiet admin screen is not evidence of a clean site.
Hold the Line with BitFire
CVE-2026-1490 turns a spam plugin into an unauthenticated software installer, but BitFire breaks it at two independent points: FREE Bot Protection refuses the scripted delivery before WordPress executes vulnerable code, and BitFire PRO RASP blocks the unauthorized plugin PHP from ever reaching disk. Install BitFire, keep the FREE bot and request defenses on, add PRO RASP for runtime enforcement, and run Threat Hunter if 6.71 ever touched your server. Update to CleanTalk 6.72 today — then let BitFire hold the line against the next one.