CVE-2024-10781 vulnerability and BitFire protection

How BitFire Blocks CVE-2024-10781: CleanTalk Anti-Spam Authentication Bypass

WordPress vulnerability research

BitFire PRO RASP blocks CVE-2024-10781, an empty-key authentication bypass that lets unauthenticated attackers install and activate arbitrary WordPress plugins.

Unauthenticated CVSS 8.1 High Arbitrary plugin installation Authentication bypass
BitFire · Vulnerability advisoryResearch published
AdvisoryCVE-2024-10781
ComponentAnti-Spam by CleanTalk – Spam Protection Without CAPTCHA
Relevant sourcelib/Cleantalk/ApbctWP/RemoteCalls.php — RemoteCalls::perform() token check
Executive summary

What WordPress administrators need to know

CleanTalk Anti-Spam 6.44 exposes an unauthenticated remote-call endpoint that is reachable on every front-end request. When the plugin's API key is empty, the endpoint's shared-secret token check compares against publicly computable digests of the empty string and passes, handing attackers administrator-equivalent plugin installation and activation from the wordpress.org catalog. On sites running an affected version, BitFire PRO RASP interrupts the attack at its decisive step: the filesystem guard blocks the unauthorized PHP plugin-file writes into wp-content/plugins, so the attacker's package never lands and cannot be activated. Version 6.45 eliminates the flaw at its source. Here is how the exploit works and exactly where BitFire stops it.

At a glance

Key facts

  • Reachable on every front-end request through the plugin's init-hooked remote-call handler, with no login or capability check.
  • An empty CleanTalk API key reduces the token gate to publicly computable empty-string digests.
  • Attackers install and activate any wordpress.org plugin without credentials, writing PHP into wp-content/plugins.
  • Remote code execution is conditional on activating a further vulnerable plugin, per the disclosure.
  • CleanTalk 6.45 adds a non-empty-key precheck and a hardened token comparison in RemoteCalls::perform().
  • BitFire PRO RASP filesystem guard blocks the unauthorized PHP write the attack depends on.
01
Vulnerability overview

Understand the exposure

The affected component, attack path, and practical risk for WordPress websites.

Affected componentAnti-Spam by CleanTalk – Spam Protection Without CAPTCHA
Potential reach200000 installations
Attack techniqueauthentication bypass
Published2026-09-29
BitFire PRO RASP stops CVE-2024-10781 at the only step that matters: the instant the exploit tries to write PHP plugin files into wp-content/plugins, BitFire blocks the unauthorized write — the package never lands, and the attack dies there.
02
Technical analysis

How the vulnerability works

Research details, affected versions, exploitation behavior, and remediation guidance.

How CVE-2024-10781 Works

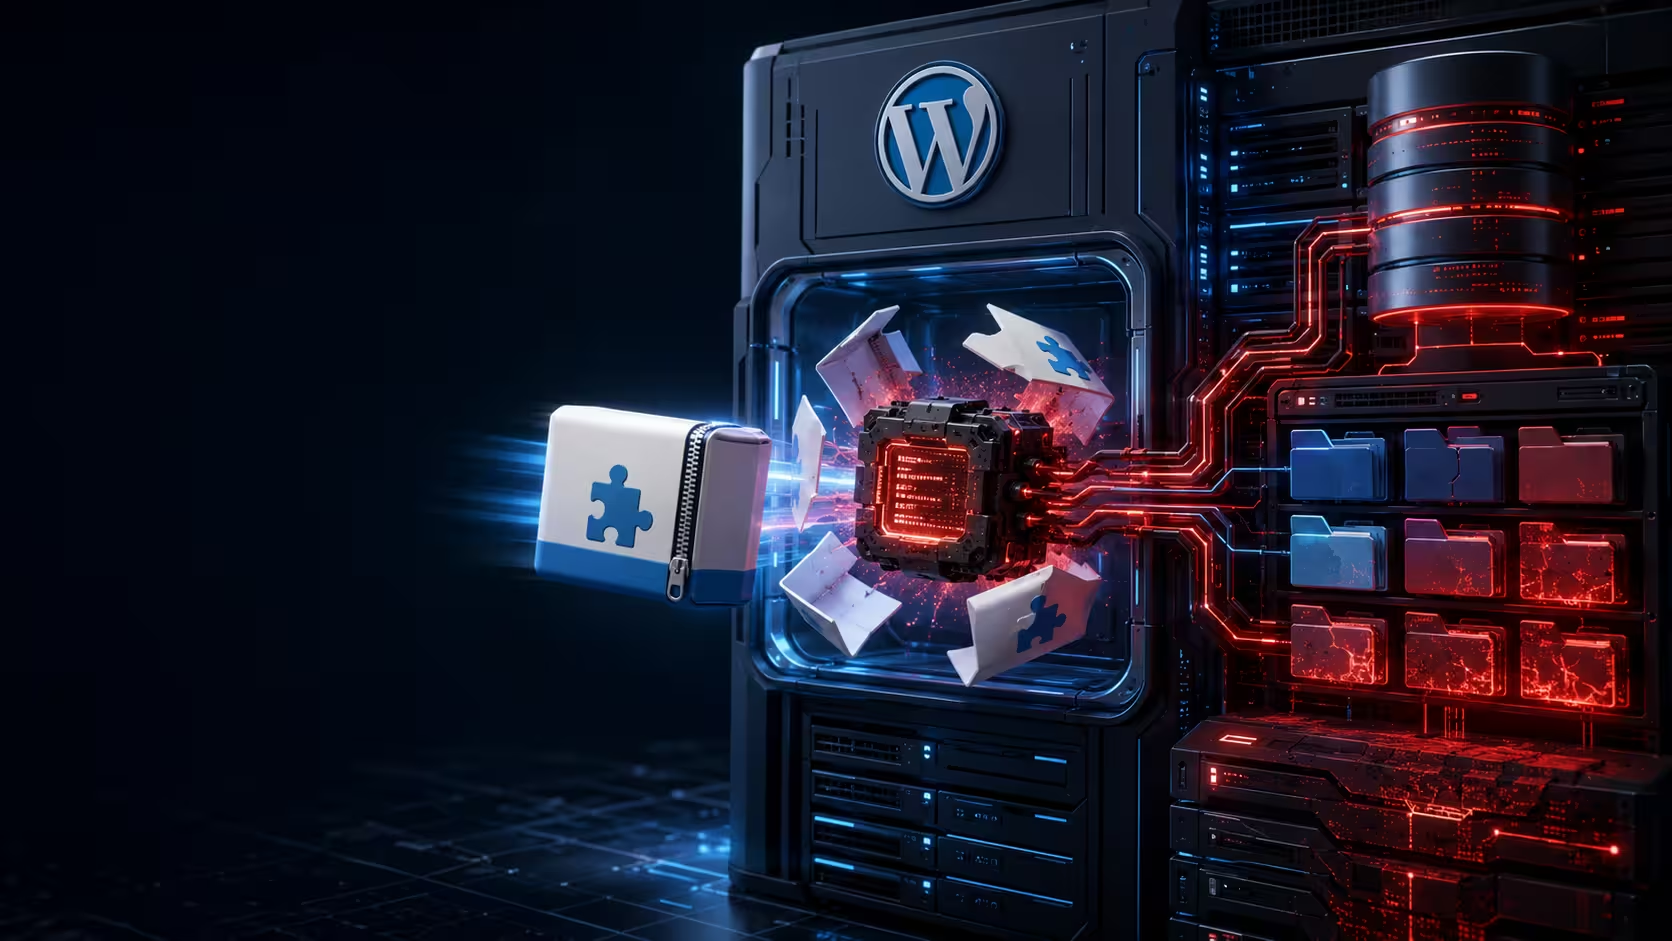
CleanTalk's remote-call interface hooks WordPress's init routine, so the handler runs on every front-end request — no login, nonce, or capability check stands in front of it. The handler compares a request-supplied token against the MD5 or SHA-256 digest of the site's CleanTalk API key. That comparison never verifies the key exists. On sites where no key is set, the matching digests are constants anyone can compute offline, and the gate opens. The attacker selects the plugin-installation action and names any plugin in the wordpress.org catalog. CleanTalk's own upgrader then writes the package — including PHP files — into wp-content/plugins and activates it, operations normally reserved for administrators. Per the disclosure, code execution is conditional on activating another vulnerable plugin; the unconditional impact is unauthorized plugin installation and full site integrity compromise.

Where BitFire PRO RASP Stops the Attack

BitFire PRO RASP is included with BitFire PRO and enforces authorization at the protected operation — and this attack has exactly one: writing PHP plugin files into wp-content/plugins. When the injected remote call reaches CleanTalk's upgrader and it attempts to create the package's PHP files, BitFire PRO RASP's filesystem guard classifies the write as unauthorized PHP creation, because no valid administrator session stands behind it, and blocks it. The attacker's chosen package never lands on disk, plugin activation has nothing to install, and the disclosure's conditional code-execution scenario collapses at its first requirement. Notably, the malicious request carries ordinary parameter values with no recognizable attack pattern. This is precisely the exploit class that runtime enforcement at the write is built to stop.

The Fix in CleanTalk 6.45

CleanTalk 6.45 closes the gate in lib/Cleantalk/ApbctWP/RemoteCalls.php. A new isRcAllowed() precheck runs before any token validation and terminates the request with a FORBIDDEN response unless the installation has a non-empty API key or a qualifying hosting license. The inline digest comparison is replaced by checkToken(), which builds its comparison secret only from a non-empty key and refuses to compare against an empty one, making the empty-string match impossible. Update to 6.45 or later immediately: the unauthenticated entry point and the install/activate code paths are unchanged, so only the repaired gate stands between an attacker and plugin installation.

If Your Site Was Affected, Investigate for Persistence.

Patching closes the known path; it does not undo a compromise that already happened. If your site ran CleanTalk 6.44 or earlier — particularly without an API key set — treat it as potentially compromised. Review your installed plugin list for anything you did not install, remove it, and rotate administrator credentials and WordPress authentication keys. Then run BitFire Threat Hunter. It performs a thorough post-compromise investigation and discovers backdoor WordPress administrator accounts, hidden database triggers, long-running PHP processes, and the droppers that can restore malware or reinfect the site. A missing suspicious file proves nothing; investigate before you consider the site clean.

Stop It at the Runtime, Not the Signature

CVE-2024-10781 turns a spam-filter plugin into an unauthenticated software installer. BitFire PRO RASP does not need to recognize the CVE: the moment the exploited remote call attempts to write PHP plugin files into wp-content/plugins, BitFire's filesystem guard blocks the unauthorized write, and the attack ends at the runtime operation it depends on. Patch to CleanTalk 6.45, investigate any site that ran an older version with BitFire Threat Hunter, and put BitFire PRO RASP in front of your WordPress filesystem today.
03
Source review

Vulnerable and fixed code

The relevant source is located in lib/Cleantalk/ApbctWP/RemoteCalls.php — RemoteCalls::perform() token check.

BeforeVulnerable behavior
// Check Access key
if (
    ($token === strtolower(md5($apbct->api_key)) ||
     $token === strtolower(hash('sha256', $apbct->api_key))) ||
    (self::checkWithoutToken() && self::isAllowedWithoutToken($action))
) {
AfterCorrected behavior
if ( ! self::isRcAllowed() ) {
    die('FAIL ' . json_encode(array('error' => 'FORBIDDEN')));
}

// Check Access key
if (
    (self::checkToken($token)) ||
    (self::checkWithoutToken() && self::isAllowedWithoutToken($action))
) {
04
Zero-day protection

Protection from the first exploit request

BitFire protects WordPress servers on day zero—before a vulnerability is publicly known and before other vendors have time to develop signatures or patches.

01 · VerifyStop unknown clients

Bot controls and browser verification stop untrusted automated clients before previously unknown exploit code reaches WordPress.

02 · DetectBlock malicious behavior

General WAF protections identify dangerous request behavior and hostile payloads without waiting for a vulnerability-specific signature.

03 · PreventContain attacks at runtime

RASP follows execution inside PHP and prevents unauthorized changes to protected files, accounts, and database content.

BitFire · WordPress protectionZero-day ready
BitFire zero-day WordPress vulnerability protection
BitFire combines verified-client controls, behavior-based WAF detection, and runtime RASP enforcement to protect WordPress before an exploit has a name, CVE, signature, or vendor patch.
About the author

Cory Marsh

Cory has more than 20 years of internet security experience and is a lead developer on the BitFire project.

Read BitFire security research →
Protect your WordPress website

Add protection before the next exploit arrives.

BitFire combines bot controls, request inspection, malware detection, and runtime protection in one WordPress security platform.

Protect my site free →